
- Healthcare AI Guidance
Can employees use ChatGPT and stay HIPAA-compliant?
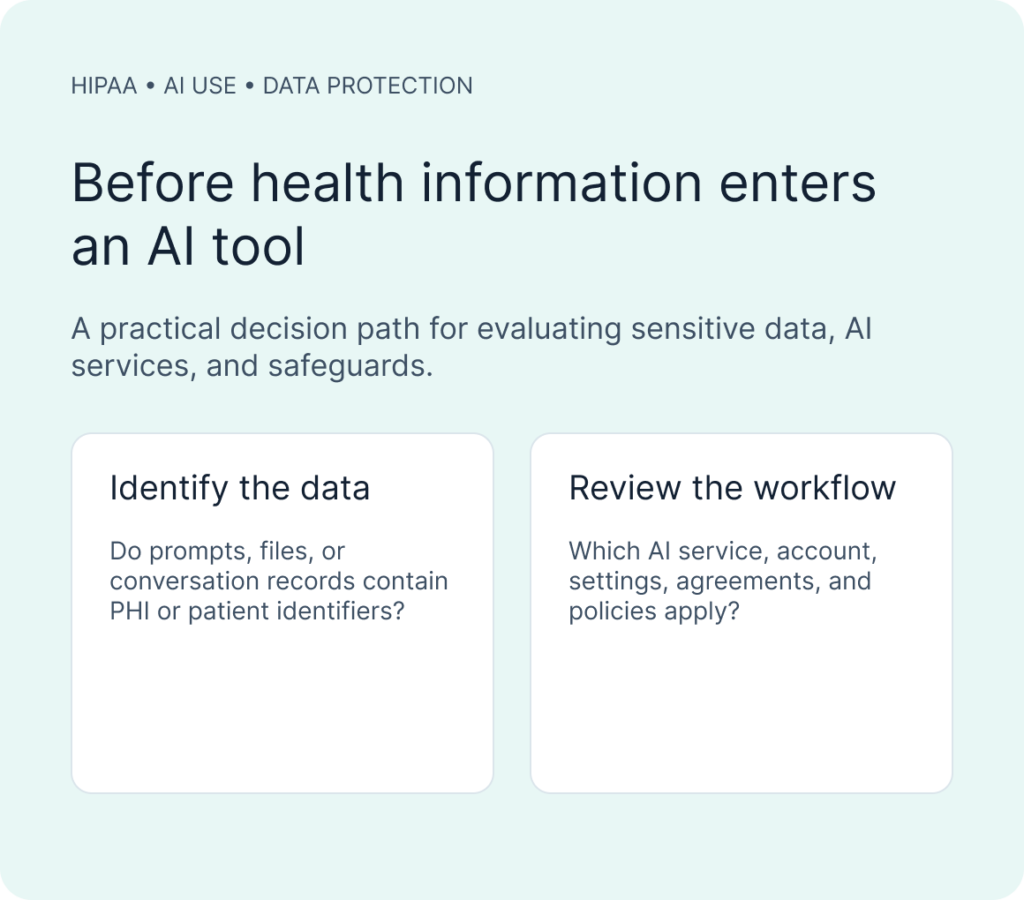
There is no blanket yes or no.
When it may be possible
Use a service and configuration reviewed and approved for the intended data and use case, with applicable agreements and safeguards.
When to pause
If PHI would be shared with a service not approved for that use, pause until privacy, security, and legal stakeholders review it.
What this cannot certify
A product or technical control alone does not make an organization HIPAA-compliant.
A six-point review before employees use ChatGPT
1. Identify PHI
Check prompts, uploaded files, outputs, and stored conversation histories.
2. Review the service
Verify product, account type, settings, terms, and intended use.
3. Confirm agreements
Determine whether a business associate agreement is required and covers the service and use.
4. Apply safeguards
Assess access controls, authentication, risk analysis, training, and technical safeguards.
5. Set retention rules
Understand storage, access, retention, deletion, and record-handling requirements.
6. Document oversight
Assign owners, review changes, maintain records, and prepare incident response.
HIPAA compliance is broader than prompt redaction.
People & policy
Define approved use cases, train employees, and provide a clear review path.
Technology & configuration
Use suitable access, data-protection, logging, and configuration controls.
Oversight & response
Review risks, document decisions, and plan for suspected exposure.
Add an AI interaction security layer - not a compliance shortcut.
Masker
Masker protects AI usage across browsers, AI gateways, desktop applications, and AI agents through a unified security and governance platform. It brings security controls together to help organizations manage AI interactions and apply policies across supported environments.
Redactor
Redactor helps protect personally identifiable information (PII) and protected health information (PHI) by redacting sensitive data in real time. It replaces sensitive information with safe, format-preserving data across supported images, documents, and PDFs before the information leaves your network.
Protector
Protector helps organizations control AI usage within employee browsers and guide users toward secure AI adoption. It supports visibility and security controls for browser-based AI workflows, helping teams manage unauthorized AI tools and reduce the risk of sensitive information being submitted through prompts.
Governor
Governor is the unified governance layer built into every layer of Masker. It supports policy enforcement, auditability, and compliance-related oversight by providing visibility into AI interactions and helping organizations identify and investigate potential policy breaches.
- Use Cases
Real-World Applications
Patient Data Exposure Through AI Tools: The Johns Hopkins Case
A recent data breach at Czech online supermarket Rohlík highlights a growing challenge for businesses: protecting the sensitive information stored
Rohlík Data Breach: The Hidden Risk of Exposed AI Conversations
A recent data breach at Czech online supermarket Rohlík highlights a growing challenge for businesses: protecting the sensitive information stored